ISO 27001 certificationSoftware with optional expert support

Bring your ISO 27001 work into one system.

AmpliFlow brings together risks, 93 controls, the SoA, ownership, nonconformities, and management follow-up. You get a project plan and optional expert support before certification. After the audit, you continue in the same software.

Free, with no preparation needed. After the call, you receive a quote with the proposed setup, support, and price.

ISO 27001
What ISO 27001 requires

Manage information security as part of the business

ISO/IEC 27001 requires an information security management system that is established, implemented, maintained, and continually improved. Its documented scope determines which parts of the organization are included. Within that scope, information security must be part of working methods, decisions, and management follow-up to protect the confidentiality, integrity, and availability of information.

Management

Management owns the work

Management sets the policy and objectives, ensures that responsibilities and resources are in place, and checks that the ISMS achieves its intended outcomes. In AmpliFlow, you keep decisions, owners, tasks, and results together.
Risks

Select controls from risk treatment

Assess each information security risk, decide how to treat it, document the required controls, and specify who can approve the decision.

The business

Management, business functions, and IT share responsibility

The ISMS covers people, processes, suppliers, physical environments, and technical systems within its defined scope. The organization decides who does what. For example, management can make decisions, affected business functions can implement working methods, and IT can monitor the selected technical safeguards. Decisions, ownership, and follow-up results are recorded in AmpliFlow.

The platform

One software platform from implementation to ongoing follow-up

During the certification project, connect controls to risks, processes, legal requirements, and governed pages with policies and procedures. After the audit, use the same platform for risk decisions, actions, objectives, nonconformities, audit results, and management review.

  • Assign an owner to each riskRecord the risk assessment, approved risk treatment, owner, and due date so the action can be followed up.
  • Use the SoA in ongoing control workAnnex A controls, justifications, status, and actions are kept in one control register.
  • Give management the evidence needed for review and decisionsCompile risk treatment, overdue actions, control status, and audit results for management review.

Screenshots showing work with risks, controls, and documents

See the work in AmpliFlow

The screenshots show a project overview, the information security control register, an operational risk analysis, and a published policy.

Control register and SoA

Assess the 93 controls and document your SoA

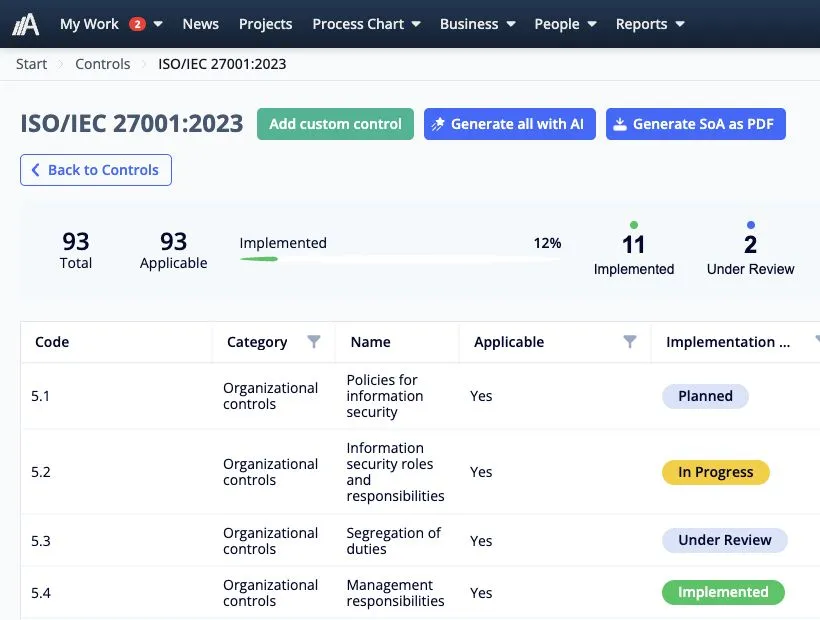
ISO/IEC 27001:2022 has 93 controls in Annex A. The AmpliFlow control register contains them, organized by code and category. Assess the controls against your approved risk treatment, legal requirements, customer requirements, and contractual requirements, and add custom controls where your business needs them.

Follow up the status and owner of each control, create tasks, and attach records such as approvals, test reports, procedures, or screenshots that show what has been completed.

Optional AI assistance can produce text drafts for you to review and edit. In the control register, you can export the Statement of Applicability (SoA) as a PDF.

Book a free call about the control work →

Annex A contains

93

controls available in the control register.

  • 93 Annex A controls
  • SoA
  • Applicability and status
  • Owners and tasks
  • Custom controls
  • SoA export to PDF and optional AI assistance
ISO 27001 controls workspace in AmpliFlow showing control status, applicability, and follow-up
The control view shows applicability, status, ownership, and follow-up together on one page.
One integrated management system

Add more ISO standards without starting over

Reuse processes, customer requirements, competence requirements, nonconformities, and objectives in the same platform. Activate only the modules you need and assess each standard's requirements separately.

Requirements, processes, and controls

Link requirements to controls

Assign each customer requirement to an owner and specify the affected processes. Link each legal requirement to the controls you assessed as contributing to compliance and record an owner, review interval, and the material to be checked.

Verify corrective actions

Follow corrective actions

Record the nonconformity, assign an owner, approve the corrective action, and document who verified its effectiveness and what evidence they reviewed.

Input for management

Prepare management review

Compile documented competence requirements, completed training, objective results, overdue actions, and current audit reports for management review.

How to get ready for certification

From defining scope to the certification audit

Build the management system step by step with risk management, controls, SoA, documentation, and follow-up. Use the same records in ongoing work after the audit.

04

Prepare for the certification audit

Close the remaining gaps and compile risk decisions, control records, internal audit results, and management-review input. A certification body conducts the external certification audit.

Mini, Midi, or Maxi

Choose how much of the implementation you want to lead yourselves

Every package includes AmpliFlow, system setup, file migration, templates, and an introduction to the software and templates. The difference is how much support you get with project leadership, internal audit, training, and adaptation. Every level requires management involvement and an internal owner.

Mini

You lead and carry out the work yourselves

For teams with an internal project lead that want to build the management system themselves on a ready-made foundation in AmpliFlow.

Included

  • AmpliFlow software
  • System setup
  • File migration
  • Templates
  • Introduction to the software and templates

Midi

You share project leadership with AmpliFlow

For teams that want to combine their own work with project leadership, internal audit, training, and help adapting the setup.

Included

  • AmpliFlow software
  • System setup
  • File migration
  • Templates
  • Introduction to the software and templates
  • Internal audit
  • Project leadership together with AmpliFlow
  • Midi training package
  • Adaptation for a simpler way of working

Maxi

AmpliFlow leads the implementation

For teams that want us to lead the implementation and adapt the system for an efficient way of working.

Included

  • AmpliFlow software
  • System setup
  • File migration
  • Templates
  • Introduction to the software and templates
  • Internal audit
  • Project leadership led by AmpliFlow
  • Adaptation for a simpler way of working
  • Maxi training package
  • Adaptation for a more efficient way of working

Not sure which package fits? We recommend a level based on your current position, available time, and internal capacity.

Book a call
FAQ

Common questions about ISO 27001

Is file migration included?
Yes. File migration is included at no extra charge, for example from SharePoint, file servers, or older systems. Together, we decide which files should move.
Does AmpliFlow replace SIEM, EDR, or other technical security tools?
No. AmpliFlow records decisions, responsibilities, controls, tasks, and follow-up for your ISMS. Technical safeguards are implemented and monitored through your selected security tools and procedures, such as IAM, EDR, and SIEM.
Can ISO 27001 be combined with other standards?
Yes. When the relevant modules are enabled, you can use the same process descriptions, customer requirements, competence requirements, nonconformities, and objectives in work with several standards. Each standard's requirements are assessed separately.
How does AmpliFlow help us become ISO 27001 certified?
Define the scope, approve risk treatment, document the SoA, implement controls, and complete an internal audit. In AmpliFlow, you compile tasks and records for management review. In Midi and Maxi, AmpliFlow can also review agreed material. An independent certification body conducts the external audit and decides whether to certify the organization.
Can we gather risks, controls, and audit records that are now in separate files?
If risks, controls, and audit material sit in separate files, you can bring them into AmpliFlow, assign ownership, and track status. After the certification audit, continue using the same risk registers, control register, and audit material in ongoing follow-up.
What is a Statement of Applicability, or SoA?
The Statement of Applicability lists the controls you have determined are necessary, why they are needed, and whether they are implemented. It also identifies the excluded Annex A controls and explains why they were excluded. You can then export the Statement of Applicability as a PDF.
Do we need to implement all 93 Annex A controls?
No. ISO/IEC 27001:2022 clauses 6.1.3 c-d require you to determine the controls needed for the selected risk treatments and then compare them with Annex A. The SoA must justify the necessary controls included and why any Annex A controls have been excluded.
Does AmpliFlow's ISO 27001 setup fit small and mid-sized companies?
The setup can fit if you have an internal lead, a clear scope, and technical security tools for the safeguards you need. Choose Mini, Midi, or Maxi based on how much project leadership, review, and audit support you want.
Free call, quote with setup and price

Book a free ISO 27001 call

You do not need to prepare anything. We start with your scope, risks, and the time your internal lead can set aside. Based on that, we propose Mini, Midi, or Maxi. After the call, you receive a quote with the proposed setup and price.